
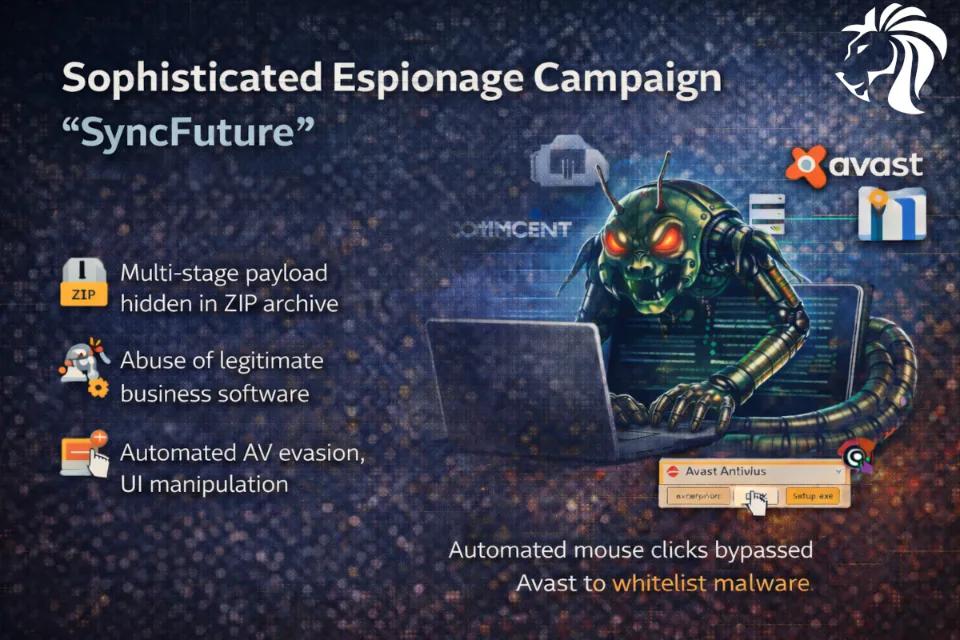
Threat researchers uncovered a highly advanced phishing and malware operation dubbed SyncFuture, targeting residents of India through emails impersonating the Income Tax Department.
Attackers abused legitimate enterprise software, Microsoft-signed binaries, and highly targeted antivirus evasion techniques to gain persistent access to infected systems — including automated UI manipulation of Avast Antivirus to whitelist malware.
This campaign highlights a worrying shift:
➡️ malware no longer just evades security tools — it interacts with them like a human user.
🛡️ A clear signal that modern espionage malware is becoming context-aware, adaptive, and product-specific.
Key Takeaways
📧 Phishing emails impersonating government entities
📦 Multi-stage malware hidden in ZIP archives
🧩 Abuse of Microsoft-signed binaries
🖱️ Automated mouse & click simulation to bypass AV
🔐 Persistence via antivirus exclusion manipulation
⚠️ Why This Matters
Security tools alone are no longer enough.
Defenders must assume attackers understand specific AV products, user interfaces, and enterprise software workflows.
👉 Behavioral detection, endpoint monitoring, and user awareness are now critical.


