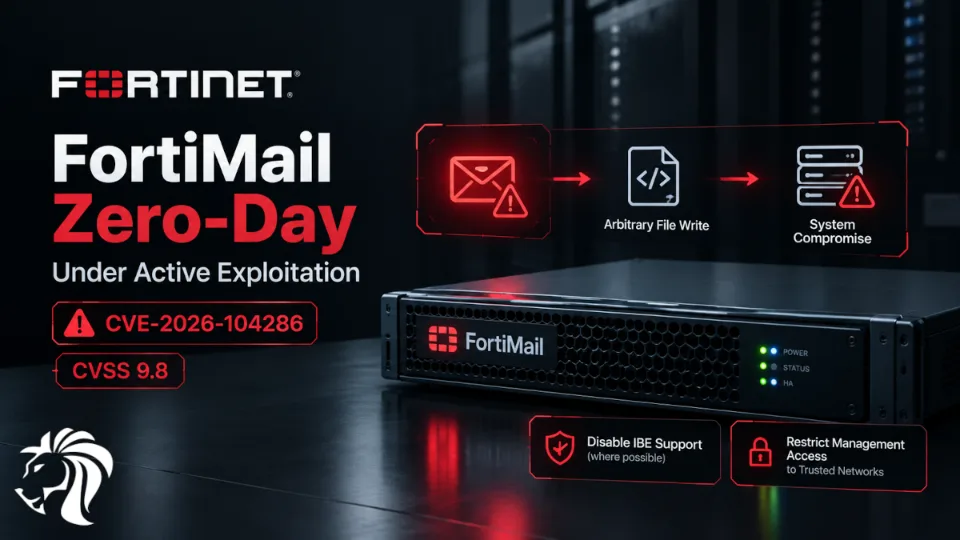
Fortinet has warned customers that a critical zero-day vulnerability in FortiMail is being actively exploited in the wild, putting internet-exposed email security gateways at immediate risk.
Tracked as CVE-2026-104286, the vulnerability carries a CVSS v3.1 score of 9.8 and allows an unauthenticated remote attacker to write arbitrary files to the underlying FortiMail system through specially crafted HTTP or HTTPS requests. The flaw combines a path-traversal weakness with improper handling of NULL characters.
For companies using FortiMail at the network perimeter, the issue is particularly serious because successful exploitation can move an attacker beyond the normal email-filtering layer and into the underlying security appliance.
An Actively Exploited Zero-Day
Fortinet disclosed the vulnerability on October 1 and confirmed that it had already been exploited in the wild. CISA subsequently added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog, with federal civilian agencies given a short remediation window.
The vulnerability does not require authentication or user interaction. An attacker can send crafted web requests to a vulnerable FortiMail interface and cause arbitrary files to be written to the underlying system.
That capability is more significant than a simple file-write vulnerability. Security researchers note that an attacker able to place or modify files on the appliance may be able to progress toward unauthorized code or command execution, depending on the files and system locations affected. Fortinet itself warns that the flaw can lead to unauthorized code or command execution.
Identity-Based Encryption at the Center
Fortinet's immediate mitigation guidance focuses on Identity-Based Encryption (IBE) support and exposure of the FortiMail management interface.
Where operationally possible, Fortinet recommends disabling IBE support. As an alternative, administrators should remove the FortiMail management interface from direct internet exposure and restrict access to trusted private networks.
This is particularly important for organizations that have historically exposed administrative interfaces for remote management. Internet accessibility significantly reduces the attacker's barrier to reaching the vulnerable functionality.
The recommended mitigation is therefore not simply an email-security configuration change. It is also an attack-surface reduction measure.
Which FortiMail Versions Are Affected?
The affected branches include:
- FortiMail 8.0.0–8.0.1
- FortiMail 7.6.0–7.6.6
- FortiMail 7.4.0–7.4.8
- FortiMail 7.2.0–7.2.9
Organizations should verify their exact FortiMail release and configuration against Fortinet's current advisory before determining exposure.
Security teams should also account for the possibility that an appliance could have been compromised before mitigation was applied. Updating or changing configuration does not by itself establish that previous exploitation did not occur.
Why Compromise Assessment Matters
FortiMail appliances sit in a sensitive position within enterprise infrastructure. They process email traffic and can contain or interact with information that is valuable to attackers.
Because CVE-2026-104286 is already being exploited, organizations should treat exposed vulnerable appliances as potential incident-response cases rather than limiting their response to vulnerability scanning.
Fortinet has published indicators of compromise to support investigations. Security teams should review relevant appliance logs, unexpected file changes, administrator activity, authentication events and outbound network connections, and compare findings with Fortinet's current indicators.
The objective should be to answer two separate questions:
Is the appliance vulnerable?
and
Was the appliance already compromised?
Both require attention.
What Companies Should Do Now
Companies operating FortiMail should prioritize several actions:
✅ Identify vulnerable appliances
Inventory FortiMail deployments, versions and management-interface exposure.
✅ Reduce external exposure
Remove management interfaces from the public internet wherever possible and restrict administrative access to trusted networks.
✅ Disable IBE where feasible
Follow Fortinet's recommended workaround if Identity-Based Encryption is not operationally required.
✅ Apply security updates
Fortinet has released security updates, and organizations should move to the appropriate fixed release as soon as possible.
✅ Hunt for compromise
Use Fortinet's indicators and review logs, system changes, administrator activity and unusual outbound connections.
✅ Treat previously exposed systems as potentially compromised
A successful configuration change or software update does not erase evidence of earlier attacker activity.
The Bigger Security Lesson
CVE-2026-104286 highlights the continuing risk posed by internet-facing security appliances.
These systems are designed to protect corporate infrastructure, but their privileged position also makes them valuable targets. A vulnerability that crosses the boundary between an externally accessible web interface and the underlying operating system can potentially turn a defensive control into an initial access point.
The FortiMail case also reinforces the importance of separating patching from incident response. When exploitation is already confirmed, organizations need both rapid remediation and a structured investigation into whether the vulnerable appliance was previously accessed.
For companies operating FortiMail, the priority is clear: reduce exposure, apply Fortinet's remediation, and investigate for signs of compromise rather than assuming that mitigation alone closes the incident.