
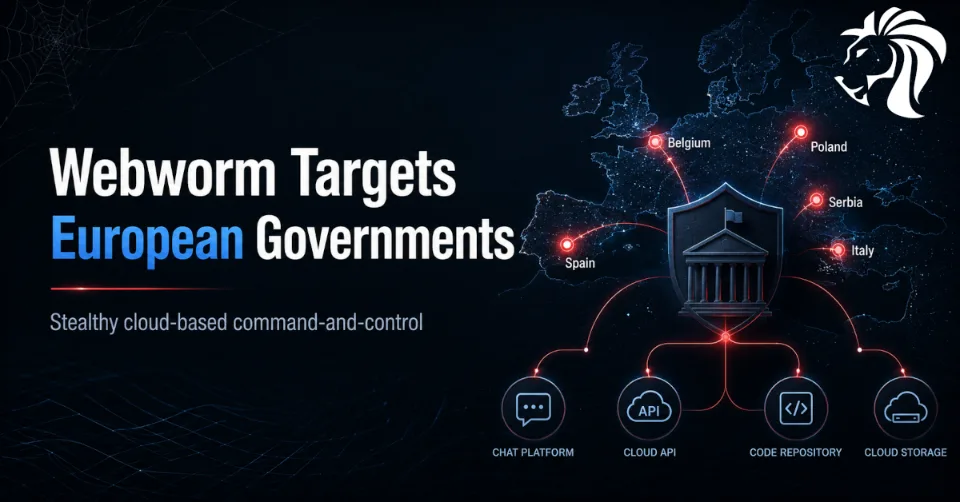
A China-linked advanced persistent threat group known as Webworm has shifted its focus to Europe, targeting government organizations and employing increasingly unusual command-and-control techniques to remain hidden within victim environments.
Recent research from ESET highlights Webworm activity against organizations in several European countries, including Belgium, Italy, Serbia, Spain, and Poland, with additional activity observed in South Africa.
The campaign shows how state-aligned threat groups are moving away from traditional malware infrastructure and toward legitimate cloud services, proxy tools, and trusted platforms such as Discord, Microsoft Graph, GitHub, and cloud storage providers.
For defenders, this creates a difficult problem: malicious traffic may blend into normal business and developer activity.
Who Is Webworm?
Webworm is a China-aligned cyber espionage group first publicly reported in 2022. At the time, its operations mainly targeted organizations in Asia.
Since then, the group’s focus appears to have expanded significantly. ESET’s latest findings suggest that Webworm is now targeting European government organizations, likely looking for access, persistence, and intelligence-gathering opportunities.
The group has evolved its tooling over time. Earlier activity involved known malware families such as McRat and Trochilus. More recent campaigns show a shift toward proxy tools, custom backdoors, cloud-hosted infrastructure, and legitimate web services used for command-and-control.
This evolution matters because well-known malware families often have signatures, infrastructure patterns, and indicators that security teams can detect. Proxy tools and legitimate cloud services are harder to identify as malicious because they can resemble normal network activity.
Why Europe Is Now in Focus
The targeting of government organizations across Europe suggests Webworm is expanding its intelligence collection priorities.
While the exact objective is not confirmed, government environments are valuable targets for cyber espionage because they may contain:
- diplomatic communications
- policy documents
- internal planning material
- procurement information
- defense or security-related data
- regional political intelligence
- access to partner organizations
- credentials or systems that can be used for further pivoting
ESET’s analysis indicates that Webworm may be looking for pivot points and initial access opportunities that allow the group to burrow deeper into networks.
This is typical of espionage-focused operations. The goal is not always immediate disruption. Often, the objective is quiet persistence, long-term access, and gradual intelligence collection.
From Traditional Malware to Proxy-Based Operations
One of the most important changes in Webworm’s activity is its increasing use of proxy tools and network tunneling solutions.
Instead of relying only on conventional backdoors, Webworm has used legitimate or semi-legitimate tools such as SoftEther VPN and SOCKS proxy solutions. The group has also used tools such as:
iox- ChainWorm
- SmuxProxy
- WormFrp
- WormSocket
These tools help attackers hide traffic, chain connections through compromised systems, and move between internal and external hosts.
Proxy-based operations are attractive to threat actors because they can:
- encrypt attacker communications
- obscure the true origin of traffic
- support internal pivoting
- blend into legitimate remote access activity
- reduce reliance on easily blocked malware infrastructure
- make attribution and detection harder
In some cases, attackers may create hidden networks by tricking victims into running proxy components that become part of the attacker’s wider infrastructure.
EchoCreep: Discord as Command-and-Control
In 2025, Webworm introduced a new backdoor called EchoCreep.
EchoCreep uses the popular chat platform Discord for command-and-control. According to ESET’s analysis, the backdoor uses Discord to upload files, send runtime reports, and receive commands.
This is a growing trend in cyber operations. Attackers use trusted platforms because traffic to those services may not immediately look suspicious. Many organizations allow access to cloud collaboration platforms, messaging tools, and developer services, making them useful channels for covert communication.
Using Discord for command-and-control can help attackers avoid detection because:
- Discord traffic may be allowed by default
- communication occurs over legitimate infrastructure
- security tools may not inspect the content deeply
- blocking the entire service may not be practical for some organizations
- each victim can be assigned a separate server or channel structure
ESET also found that Webworm used crafted HTTP requests to pass network communications through Discord’s API.
GraphWorm: Abusing Microsoft Graph and OneDrive
Webworm’s second new backdoor is GraphWorm.
GraphWorm relies on the Microsoft Graph API and OneDrive endpoints to receive tasks and upload victim information.
This technique is particularly concerning for enterprise environments because Microsoft 365 traffic is common and often trusted. Many organizations depend heavily on Microsoft Graph, OneDrive, Teams, SharePoint, and other Microsoft cloud services.
Malicious use of Microsoft Graph can be difficult to distinguish from legitimate business activity unless organizations monitor behavior carefully.
GraphWorm reportedly uses separate OneDrive directories for each victim, helping the attackers organize operations and reduce overlap between compromised environments.
This approach reflects a broader shift in attacker behavior: command-and-control is moving into trusted cloud ecosystems.
GitHub and S3 Used for Staging and Configuration
Webworm has also used GitHub repositories to stage malware and tools, allowing attackers to download components onto victim systems when needed.
In addition, ESET observed Webworm using its custom proxy solution WormFrp to retrieve configurations from a compromised Amazon S3 bucket.
This use of public and cloud-hosted infrastructure makes detection more complex. GitHub and AWS are widely used across organizations, especially in development, cloud, and IT environments. Traffic to these platforms may not trigger immediate suspicion.
For defenders, this means it is not enough to block known malicious domains. Security teams need to understand which processes are communicating with cloud services and whether that behavior is expected.
Initial Access Remains Unclear
The initial access vector for Webworm’s recent operations is not fully confirmed.
However, ESET noted that the group uses open-source vulnerability scanners to scrape web server files and directories for weaknesses in target environments. This suggests Webworm may be exploiting exposed vulnerabilities before deploying backdoors and proxy tools.
This aligns with common APT behavior. Attackers often begin by identifying exposed systems, vulnerable applications, misconfigured services, or weak internet-facing infrastructure.
Once inside, they deploy stealthier tooling for persistence, command-and-control, and lateral movement.
Why These Techniques Are Hard to Detect
Webworm’s approach is difficult for defenders because it relies heavily on services and tools that may appear legitimate.
Security teams may see traffic to:
- Discord
- Microsoft Graph
- OneDrive
- GitHub
- Amazon S3
- SoftEther VPN
- cloud-hosted proxy infrastructure
None of these is inherently malicious.
The challenge is context. The key question is not only “Is this destination bad?” but also:
- Which process is making the connection?
- Is this application expected to use Discord or Microsoft Graph?
- Is the user role consistent with this traffic?
- Is data being uploaded unexpectedly?
- Are there unusual volumes, timing patterns, or destinations?
- Is the process running from an unusual path?
- Is a server communicating with a service it has never used before?
Detection must move from simple indicator matching to behavioral analysis.
Defensive Recommendations
Organizations, especially government agencies and public-sector partners, should use this activity as a reminder to review external exposure and cloud service monitoring.
Recommended actions include:
- patch internet-facing systems quickly
- reduce unnecessary public exposure of web services
- scan for vulnerable applications before attackers do
- monitor outbound traffic to Discord, Microsoft Graph, OneDrive, GitHub, and S3
- review which processes are communicating with cloud APIs
- alert on unusual data uploads to collaboration or storage platforms
- monitor for unexpected proxy tools and VPN services
- restrict unauthorized use of SoftEther VPN and SOCKS proxies
- inspect suspicious port forwarding activity
- hunt for unknown binaries using names similar to proxy or tunneling tools
- review endpoint telemetry for unusual process chains
- segment sensitive government and administrative systems
- enforce least privilege across accounts and service access
- maintain strong logging for Microsoft 365 and cloud APIs
- review ESET’s published indicators of compromise where applicable
Where business operations allow, organizations should restrict access to services like Discord from government or high-security networks unless there is a clear operational requirement.
What to Monitor
Security teams should pay special attention to unusual communication patterns involving non-standard processes.
Examples include:
- a system process communicating with Discord
- a server making unexpected Microsoft Graph API calls
- endpoint tools uploading data to OneDrive without user interaction
- command-line tools contacting GitHub repositories
- unknown binaries connecting to cloud servers
- unexpected use of SoftEther VPN
- long-running proxy processes
- repeated outbound connections to unfamiliar cloud infrastructure
- data transfers to S3 buckets not owned by the organization
The most useful detection strategy is to combine endpoint telemetry, network logs, cloud audit logs, and identity activity.
Final Thoughts
Webworm’s recent activity shows how modern espionage groups are adapting their command-and-control methods.
Instead of relying only on traditional malware infrastructure, attackers are increasingly using legitimate cloud platforms, messaging services, APIs, and proxy tools to hide in normal network traffic.
For European government organizations, this campaign is a reminder that cyber espionage is not only about malware detection. It is about understanding how trusted services can be abused.
The defensive priority is clear: patch exposed systems, reduce attack surface, monitor unusual cloud communications, and investigate non-standard processes talking to platforms like Discord, Microsoft Graph, GitHub, and S3.
In today’s threat landscape, legitimate services can become covert channels. Defenders must watch not just where traffic goes, but why it is going there.


