
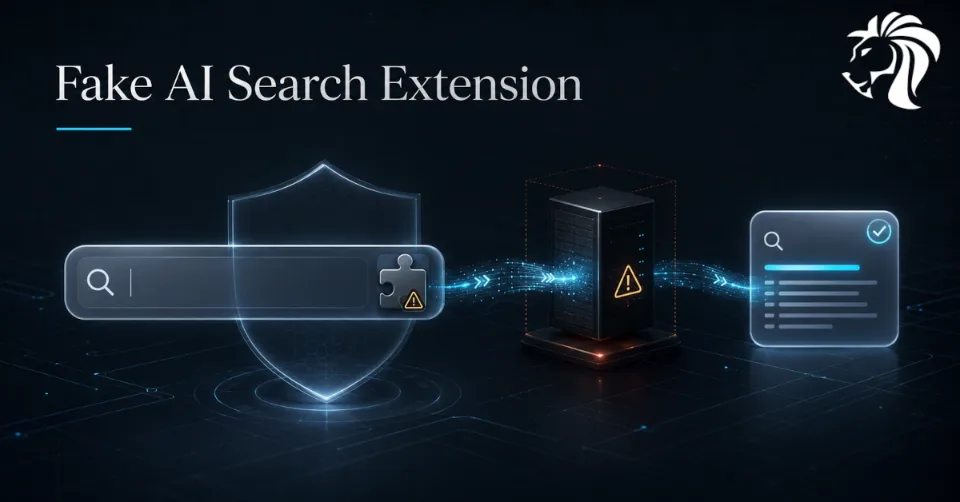
Microsoft has identified a malicious Chrome extension that impersonated the AI search engine Perplexity and quietly collected users’ search activity.
The extension, called “Search for perplexity ai”, used the ID flkebkiofojicogddingbdmcmkpbplcd and relied on a look-alike domain, perplexity-ai[.]online, to appear connected to the legitimate Perplexity service at perplexity.ai.
According to Microsoft’s Defender research team, Google removed the extension from the Chrome Web Store after responsible disclosure.
The goal of the extension was simple: intercept search activity and collect data before redirecting users to real search results.
How the Extension Worked
Once installed, the extension changed the browser’s default search engine.
From the user’s perspective, searches still appeared to work normally. Results were eventually shown through real search engines such as Perplexity, Google, or Bing.
But before that happened, the query was routed through the attacker-controlled domain perplexity-ai[.]online.
That first stop allowed the attacker’s server to log:
- the search query
- browser headers
- IP address
- user agent
- other request metadata
After logging the data, the server redirected the user to a legitimate search engine.
This made the attack harder to notice because the final result looked normal.
The theft happened silently before the redirect.
The Address Bar Made It Worse
The extension did not only collect completed searches.
It also abused Chrome’s live search suggestion functionality.
By setting the browser’s suggest_url to the attacker-controlled domain, the extension could receive address bar input before the user pressed Enter.
That means the attacker could potentially see not only final search terms, but also every character typed into the address bar while suggestions were being generated.
This is a serious privacy issue.
Users often type sensitive fragments into the address bar, including internal company names, customer references, personal questions, partial URLs, error messages, or security-related searches.
Even if passwords were not confirmed stolen, the extension had access to far more information than a search tool should ever need.
Why This Was Not Just a Redirect
Chrome allows extensions to override search providers. Many legitimate extensions use this capability.
The suspicious part is what this extension did with that access.
Instead of simply forwarding users to a search provider, it routed traffic through infrastructure controlled by the attacker.
Microsoft also found that the extension requested permissions from the declarativeNetRequest family, which can be used to modify and redirect browser traffic.
The extension also shipped server-side logic that logged every request.
That matters because it suggests the collection was deliberate, not an accidental side effect of a search redirect.
The extension reportedly included disabled redirect rules for Google and Bing as well, meaning the same mechanism could potentially be expanded to other search engines.
It also contained room to execute WebAssembly code later, which is unnecessary for a simple search extension and raises further concern about possible future capabilities.
AI Branding Is Becoming a Malware Lure
This incident fits a wider trend: malicious browser extensions hiding behind AI branding.
Attackers know that users are actively looking for AI tools, assistants, search helpers, browser companions, and productivity extensions.
That creates an opportunity.
A fake AI-branded extension can appear useful, familiar, and low risk. Once installed, it can request browser permissions, change search behavior, monitor web activity, or collect sensitive input.
Microsoft has previously linked other AI-themed malicious extensions to chat-skimming activity involving services such as ChatGPT and DeepSeek.
In those cases, attackers focused on conversations inside AI platforms.
This Perplexity-themed extension was different.
Its target was broader: user searches and address bar input.
That makes it especially concerning because the browser address bar is one of the most heavily used input fields on any device.
Why Search Data Is Valuable
Search queries can reveal a lot about a person or organization.
For individuals, they may expose:
- health concerns
- financial questions
- legal issues
- personal interests
- location-based activity
- private research topics
For companies, search activity may reveal:
- internal tools
- customer names
- project names
- infrastructure details
- vendor relationships
- security incidents
- error messages
- business strategy
Even without passwords, this kind of data can support profiling, phishing, reconnaissance, and targeted attacks.
A malicious extension does not need full account takeover to create risk.
Sometimes metadata and search behavior are enough.
What Users Should Do
Anyone who installed “Search for perplexity ai” should remove it immediately.
Users should also check whether their default search engine has been changed.
Recommended steps:
- remove the suspicious extension
- review all installed Chrome extensions
- check the default search engine setting
- reset search provider settings if needed
- clear suspicious browser permissions
- watch for unexpected redirects
- avoid extensions using look-alike AI branding
Users should also be cautious with any extension that asks to change search settings or route browsing activity through an unfamiliar domain.
A search extension should not need broad control over browser traffic.
What Security Teams Should Monitor
For organizations, the risk is larger because browser extensions can spread quietly across many endpoints.
Security teams should watch for:
- unauthorized Chrome extensions
- changed default search providers
- suspicious extension permissions
- browser traffic to unfamiliar domains
- look-alike domains imitating AI services
- unexpected use of declarativeNetRequest permissions
- extensions that redirect search traffic
- unusual address bar suggestion endpoints
Organizations should also consider using browser management policies to allow only approved extensions.
This is especially important for AI-branded tools, where employee interest may be high and attacker impersonation is increasingly common.
Recommended Defensive Controls
Microsoft’s guidance focuses on basic but important controls:
- allow only approved extensions
- enforce browser extension policies
- review extension permissions
- monitor search provider changes
- inspect suspicious browser redirects
- block known malicious or look-alike domains
- educate users about fake AI tools
- verify publisher identity before installation
- prefer official vendor links over store search results
For companies, extension control should be treated as part of endpoint security.
Browsers are now a major work platform, and extensions can become a direct path into sensitive data.
Final Thoughts
The fake Perplexity AI Chrome extension shows how attackers are adapting to the popularity of AI tools.
The extension did not need to exploit a browser vulnerability or steal passwords to create risk.
It used Chrome’s own extension capabilities to change the search provider, intercept queries, collect address bar input, and redirect users to legitimate results so the activity looked normal.
The AI branding helped win trust.
The search override enabled the data collection.
The lesson is clear: browser extensions should be treated like software with real security impact, especially when they request control over search settings, redirects, or browsing data.


