
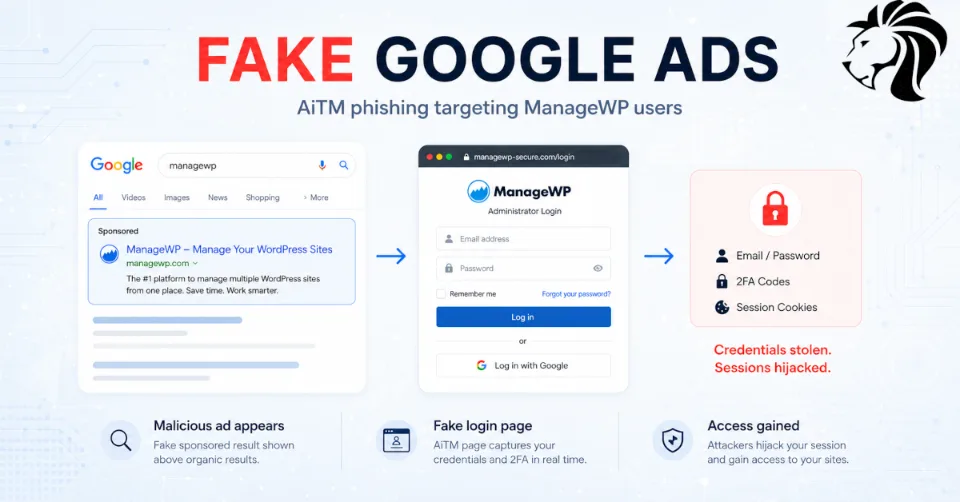
A new phishing campaign is abusing Google-sponsored search results to steal credentials for ManageWP, GoDaddy’s platform for managing multiple WordPress websites from one central dashboard.
According to reporting based on Guardio Labs’ findings, the malicious sponsored result can appear above the legitimate ManageWP result for the search term “managewp.” This is especially dangerous because many users still search Google for login pages instead of typing the official URL directly or using bookmarks.
Why ManageWP Is a High-Value Target
ManageWP is used by web developers, agencies, enterprises, and administrators to manage fleets of WordPress sites from a single panel. That makes it a valuable target because one compromised account may provide access to many websites at once.
Guardio Labs head researcher Nati Tal told BleepingComputer that a typical ManageWP account can host hundreds of sites. WordPress.org statistics also show that the ManageWP Worker plugin is active on more than 1 million websites, meaning account compromise could have a large downstream impact.
How the Attack Works
The attack starts when a user searches for ManageWP and clicks the malicious sponsored result instead of the legitimate login page.
The victim is taken to a fake login page that looks almost identical to the real ManageWP portal. When the user enters their credentials, those credentials are sent to a Telegram channel controlled by the attacker.
But this is not just a basic credential-harvesting page.
The campaign uses an adversary-in-the-middle, or AiTM, setup. That means the attacker uses the stolen credentials in real time to log into the legitimate ManageWP service while the victim is still interacting with the fake page.
2FA Is Also Targeted
After the username and password are captured, the victim is shown a fake prompt asking for their two-factor authentication code.
The attacker then uses that 2FA code immediately to complete the login process and gain access to the real ManageWP account.
This is why traditional 2FA is important but not always enough. If a user types a one-time code into an AiTM phishing page, the attacker may be able to use it before it expires.
Operator-Driven Phishing
Guardio Labs reportedly infiltrated the attacker’s command-and-control infrastructure and observed a dropdown-based command system that allowed the attacker to steer phishing sessions interactively.
This suggests the campaign is not a simple automated phishing page. It appears to be an operator-driven phishing framework, where the attacker can respond dynamically depending on what the victim does.
Tal also said the platform does not appear to be a commodity phishing kit, but rather a private phishing framework. Researchers also found a Russian-language agreement embedded in the code, including an illegal-use disclaimer and a restriction against using the panel against Russia-based systems.
Confirmed Victims
Guardio Labs captured victim data from the attacker's infrastructure and began contacting exposed users. At the time of reporting, researchers had confirmed 200 unique victims.
Even that number should be treated seriously because ManageWP accounts often control multiple WordPress sites.
A single compromised account could potentially lead to:
- WordPress admin access abuse
- malicious plugin or theme installation
- SEO spam injection
- credential harvesting pages hosted on compromised sites
- backdoor deployment
- client site defacement
- supply-chain impact across agency-managed websites
Why Sponsored Search Results Are Risky
This campaign highlights a common user behavior that attackers continue to exploit: searching for login pages.
Sponsored search results may appear above the real results, and users often click the first visible link without checking the domain carefully. That gives attackers a powerful way to intercept users before they even reach the legitimate website.
The risk is especially high for platforms used by administrators, developers, web agencies, finance teams, and SaaS operators.
How ManageWP Users Can Protect Themselves
Anyone using ManageWP should take immediate precautions:
- Use a saved bookmark for the official ManageWP login page.
- Avoid sponsored search results for login portals.
- Check the full domain before entering credentials.
- Use a password manager, because it will usually not autofill credentials on fake domains.
- Review recent ManageWP account activity.
- Rotate credentials if suspicious activity is suspected.
- Re-check 2FA settings and recovery methods.
- Review all connected WordPress sites for unknown users, plugins, themes, or file changes.
- Consider phishing-resistant authentication where available.
Guidance for Agencies and WordPress Administrators
For agencies and teams managing many client websites, this type of attack should be treated as a high-impact risk.
Recommended actions:
- Create internal bookmarks or SSO tiles for admin platforms.
- Train staff not to search Google for login pages.
- Use password managers across the team.
- Monitor for new admin accounts on managed WordPress sites.
- Audit plugin and theme changes.
- Restrict who can access ManageWP.
- Separate client environments where possible.
- Enable alerts for suspicious site changes.
- Review logs after any suspected credential exposure.
User Awareness Message
A simple message for teams:
🚨 Do not use Google sponsored results to access admin portals. Use bookmarks, password managers, or trusted internal links. If a login page asks for credentials or 2FA unexpectedly, stop and verify the domain first.
Final Thoughts
This campaign shows how attackers are moving closer to the point of trust.
They are not only sending phishing emails. They are buying visibility in search results, impersonating trusted login portals, and using AiTM infrastructure to capture credentials and 2FA codes in real time.
🔐 For admin platforms, the safest login path is not search. It is a verified bookmark or trusted internal link.
For ManageWP users, web agencies, and WordPress administrators, this is a strong reminder that one compromised account can expose many websites at once.


