
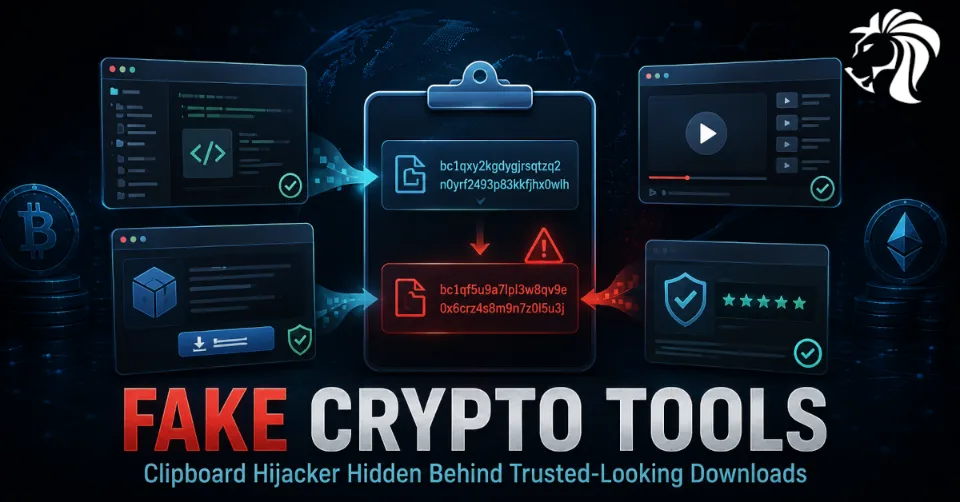
Cybercriminals have built an elaborate global reputation network to distribute cryptocurrency-stealing malware across Windows and macOS devices.
The campaign, uncovered by Check Point Software, uses a wide range of trusted-looking online assets, including GitHub repositories, SourceForge projects, fake YouTube videos, WordPress phishing sites, bogus comments, manipulated reputation signals, and even promotional content on legitimate news websites.
The goal is simple: convince users that they are downloading helpful crypto-related tools, while silently delivering clipboard-hijacking malware designed to steal cryptocurrency transactions.
The campaign shows a major shift in malware distribution. Attackers are no longer relying only on suspicious websites, spam emails, or obvious fake downloads. Instead, they are building entire ecosystems of false trust across platforms that users and even security tools may treat as credible.
A Campaign Built Around False Trust
The attackers are targeting users looking for shortcuts, quick profits, and automated advantages in cryptocurrency trading or online crash-game gambling.
The fake tools are promoted as software that can supposedly provide an “unfair advantage,” such as decryptors, predictors, automated trading helpers, or utilities that claim to improve the user’s chance of profit.
These promises are designed to attract crypto owners, traders, gamblers, and users willing to install software from unofficial sources if they believe it may help them earn money.
The malware itself is not the most unusual part of the campaign. Clipboard hijackers are a known threat. What makes this operation stand out is the amount of effort attackers put into making the downloads appear legitimate.
The Malware: A Rust-Based Clipboard Hijacker
The final payload is a Rust-based clipboard hijacker with both Windows and macOS versions.
Clipboard hijacking malware monitors what users copy and paste. When it detects a cryptocurrency wallet address, it replaces that address with one controlled by the attacker.
The victim may believe they are sending funds to the correct wallet, but the transaction is redirected to the criminal’s wallet instead.
Because cryptocurrency transactions are usually irreversible, this type of malware can cause immediate and permanent financial loss.
The campaign targets several cryptocurrencies and blockchain ecosystems, including:
- Bitcoin
- Ethereum
- Monero
- Binance Chain
- Solana
- other wallet formats and platforms
The malware also maintains persistence on the infected device, allowing it to continue monitoring clipboard activity after installation.
Why Clipboard Hijackers Are Effective
Clipboard hijackers are dangerous because they exploit normal user behavior.
Many cryptocurrency users copy and paste wallet addresses rather than typing them manually. Wallet addresses are long, complex, and difficult to verify character by character.
Attackers rely on the fact that most victims only check the first few or last few characters of the address, or do not check at all.
If the substituted address looks similar enough, the victim may approve the transaction without realizing anything changed.
This makes clipboard hijacking especially effective against users who regularly move crypto between wallets, exchanges, and payment platforms.
Fake WordPress Hub as the Campaign Center
At the center of the campaign is a WordPress-based phishing site.
The site promotes fake cryptocurrency-related tools and claims they can help users gain an advantage in trading or gambling.
The page is designed to look like a legitimate project portal, giving users enough confidence to download the offered tools.
But the WordPress site is only one part of the larger trust-building network.
The attackers also created supporting assets across other platforms to make the tools appear widely used, positively reviewed, and safe.
GitHub and SourceForge Used for Legitimacy
The attackers created GitHub repositories and SourceForge projects to promote the fake tools.
These platforms are often trusted by technical users because they are associated with open-source software and developer communities.
To strengthen the illusion, fake accounts posted positive feedback and supportive comments.
This gives the project the appearance of community interest and legitimacy.
A user who sees a tool promoted on a WordPress site, then finds matching GitHub or SourceForge pages with positive comments, may be more likely to trust the download.
That is exactly what the attackers want.
Fake YouTube Promotion With AI Narrators
The campaign also includes a dedicated YouTube channel.
According to Check Point, the videos use AI-generated narrators, suspicious view spikes, and highly positive comments that appear coordinated.
This creates another layer of false credibility.
A victim may search for the tool, find a YouTube video demonstrating it, see positive comments, and assume the software is real.
The use of AI-generated narration also lowers the cost of producing convincing promotional content. Attackers can quickly create tutorial-style videos that sound professional enough to persuade users.
Manipulating VirusTotal Reputation
One of the most concerning parts of the campaign is the apparent manipulation of VirusTotal reputation signals.
VirusTotal is commonly used by security researchers, analysts, and cautious users to check whether a file or URL appears malicious.
In this campaign, some samples received benign votes and “safe” comments, creating a misleading impression of legitimacy.
Combined with low detection rates, these reputation signals can influence users and even reputation-based detection systems.
This is a major warning for defenders: public reputation signals can be manipulated.
A “safe” comment or low detection score should not be treated as proof that a file is trustworthy.
Fake News Articles on Legitimate Sites
The attackers also promoted the fake tools through articles appearing on legitimate online news websites.
These stories advertised the supposed release of the tool and linked back to the phishing page.
It remains unclear whether the attackers used paid advertisements that were later removed, compromised news outlets, or a malicious promotion service that places fraudulent content on real websites.
Either way, the tactic adds another trust layer.
If a user sees a tool promoted on a news website, then finds it on GitHub, SourceForge, YouTube, and VirusTotal with positive-looking signals, they may believe the software is legitimate.
This is reputation laundering at scale.
Why This Campaign Is Different
Many malware campaigns rely on one or two delivery channels: phishing emails, fake download sites, cracked software portals, or malicious ads.
This campaign is different because it builds a full online reputation ecosystem.
The attackers combine:
- phishing websites
- GitHub repositories
- SourceForge projects
- fake user reviews
- AI-generated YouTube videos
- suspicious view boosting
- coordinated positive comments
- manipulated VirusTotal reputation
- promotional content on news sites
Each element supports the others.
The result is a campaign that can appear credible from multiple angles, even though the underlying tool is malicious.
A Shift in Malware Distribution
This campaign shows that attackers are adapting to how users evaluate trust online.
Many users no longer rely on a single signal. They check whether a tool appears on GitHub, whether there are YouTube tutorials, whether others have commented positively, whether VirusTotal shows detections, and whether news sites mention it.
Attackers are now manipulating all of those signals.
This creates a new problem for defenders: reputation itself can become adversarial.
Security teams cannot assume that community feedback, platform presence, or public comments are reliable indicators of safety.
Risk to Enterprises
Although the campaign appears focused on individual crypto users, enterprises should still pay attention.
Employees may use personal devices for work, access corporate systems from unmanaged endpoints, or download risky tools on company devices.
A clipboard hijacker may target crypto addresses, but the same delivery methods could be used for other malware families, including stealers, loaders, ransomware precursors, or remote access Trojans.
The broader lesson applies directly to enterprise security.
Corporate users can still be tricked by well-promoted fake tools, especially when those tools appear on platforms they recognize.
What Users Should Watch For
Users should be cautious of any software that promises guaranteed profits, crypto prediction, automated trading success, gambling advantage, or secret decryptor capabilities.
Warning signs include:
- tools promising unrealistic financial returns
- “predictor” tools for crypto or crash games
- downloads promoted through multiple suspicious channels
- YouTube videos with generic AI narration
- overly positive comments
- sudden view spikes
- GitHub or SourceForge projects with little real development history
- downloads from WordPress pages instead of official vendors
- VirusTotal comments that look coordinated
- requests to disable security tools
- unsigned or poorly documented binaries
The best protection is skepticism.
If a tool claims to provide guaranteed profit or an unfair advantage, it is likely a lure.
Defensive Recommendations for Individuals
Crypto users should take extra care before installing any trading or wallet-related software.
Recommended steps include:
- download software only from official sources
- avoid tools promising automated profits or prediction advantages
- verify wallet addresses before confirming transactions
- check the full destination address, not only the first or last characters
- use hardware wallets where possible
- test large transfers with a small transaction first
- keep endpoint protection enabled
- avoid running unknown executables
- be cautious with GitHub or SourceForge projects from unknown developers
- do not rely solely on VirusTotal comments or detection counts
- keep operating systems and browsers updated
For high-value crypto transactions, using a separate clean device may reduce risk.
Defensive Recommendations for Organizations
Security teams should treat online reputation signals as potentially adversarial.
Recommended controls include:
- monitor for clipboard-hijacking behavior
- detect clipboard listeners interacting with cryptocurrency wallet patterns
- block execution of unknown tools from user download folders
- monitor suspicious Rust-based binaries
- inspect outbound connections from newly downloaded software
- educate users about crypto scams and fake trading tools
- restrict installation of unapproved software
- use endpoint detection for persistence mechanisms
- monitor for suspicious GitHub, SourceForge, and file-hosting downloads
- review alerts that users dismiss because of “safe” online comments
- treat VirusTotal reputation as context, not proof
Organizations with employees handling cryptocurrency, treasury operations, Web3 assets, or digital wallets should be especially cautious.
Why Reputation-Based Detection Needs Caution
Reputation systems are useful, but this campaign shows they can be gamed.
Attackers can create accounts, post comments, inflate views, submit benign votes, build fake project histories, and cross-promote malicious tools across platforms.
This can influence both users and automated systems that rely heavily on reputation.
Defenders should use reputation as one signal among many, not as a final decision point.
Behavioral analysis is more important.
A file that watches the clipboard, searches for wallet patterns, maintains persistence, and communicates externally should be treated as suspicious regardless of how many positive comments it has online.
Final Thoughts
This campaign demonstrates a new level of trust manipulation in malware distribution.
Cybercriminals created an entire reputation network across GitHub, SourceForge, YouTube, VirusTotal, WordPress, and legitimate news websites to convince users that their fake crypto tools were safe and useful.
The final payload, a Rust-based clipboard hijacker, is designed to steal cryptocurrency by replacing wallet addresses during transactions.
The malware is dangerous, but the bigger story is the delivery model.
Attackers are no longer only hiding malware. They are manufacturing trust.
For users and defenders, the lesson is clear: online popularity, positive comments, GitHub presence, YouTube tutorials, and low detection rates do not guarantee safety.
When money is involved, especially cryptocurrency, skepticism is a security control.


