
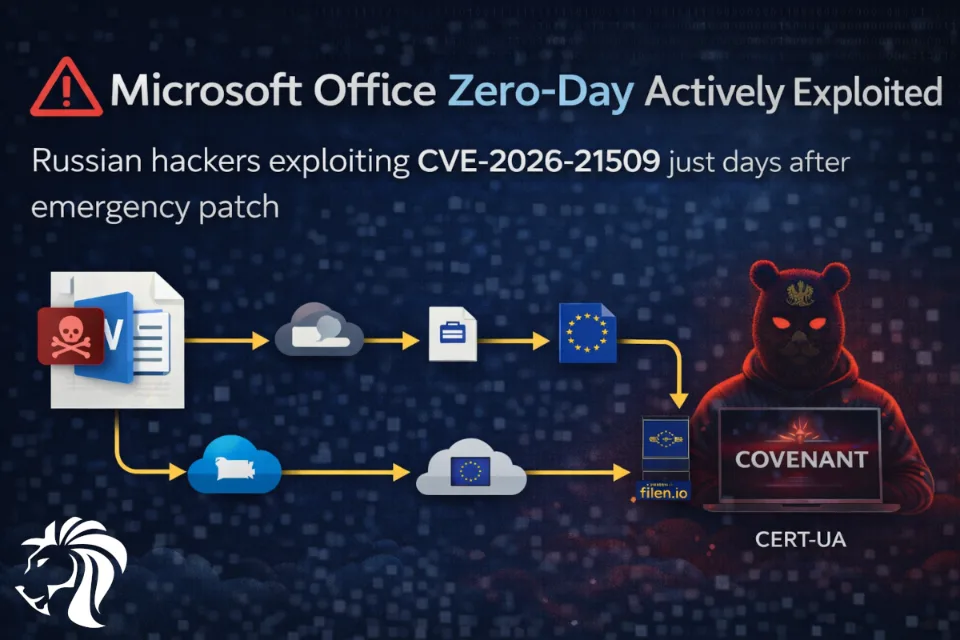
Ukraine’s CERT-UA has confirmed active exploitation of CVE-2026-21509, a recently patched zero-day vulnerability affecting multiple versions of Microsoft Office.
🗓️ Microsoft released an emergency out-of-band update on January 26, marking the flaw as actively exploited. Just days later, CERT-UA detected malicious DOC files abusing the vulnerability in targeted phishing campaigns.
🎯 Observed lures & targeting
- EU COREPER consultation themes related to Ukraine
- Emails impersonating the Ukrainian Hydrometeorological Center
- Over 60 government-related recipients targeted
🕵️ Attribution
CERT-UA attributes the activity to APT28 (aka Fancy Bear / Sofacy), a Russian state-linked threat actor associated with the GRU.
🧬 Attack chain overview
- Malicious DOC triggers a WebDAV download chain
- COM hijacking loads a rogue DLL (EhStoreShell.dll)
- Shellcode hidden in an image file (SplashScreen.png)
- Persistence via a scheduled task (OneDriveHealth)
- Final payload: COVENANT malware framework
☁️ C2 infrastructure
COVENANT communicates via filen.io cloud storage — a notable detection and blocking opportunity.
🌍 Wider impact
Subsequent attacks using similar documents were observed against EU-based organizations, confirming the campaign extends beyond Ukraine.
🛡️ Defensive actions
- Apply the latest Microsoft Office updates immediately
- Ensure Office apps are restarted to activate protections
- If patching isn’t possible, apply registry-based mitigations
- Enforce Protected View for internet-origin documents
- Monitor or block suspicious filen.io connections


